Manual App Registration in Microsoft Entra ID
Manual Registration of the EdbMails application in Microsoft Entra ID (Azure Active Directory) allows administrators to configure the required application settings and establish an OAuth-based connection between EdbMails and Microsoft 365 services. This option is suitable for organizations that prefer to manually manage application registration, API permissions, and authentication settings within their Microsoft 365 environment.
EdbMails uses OAuth-based authentication to securely connect with Microsoft 365 during migration. Both automatic registration and manual registration use OAuth authentication to authorize access. The difference is that manual registration allows administrators to configure the required Entra ID application settings themselves.
Depending on the migration requirements, administrators can choose between the Legacy Method (Exchange Web Services - EWS) and the Modern Method (Microsoft Graph API). The Legacy Method uses OAuth authentication with Exchange Web Services, while the Modern Method uses Microsoft Graph API permissions through a Microsoft Entra ID application registration.
For manual registration, the EdbMails application must first be registered in Microsoft Entra ID, required API permissions must be configured, and a client secret must be generated. Microsoft Entra ID app registration requires an account with Global Administrator privileges or the required permissions to register applications and grant consent. After completing the registration, the generated application details can be entered in EdbMails. To connect and authenticate within EdbMails, you can use either a Global Administrator account or an account with the required Full Access mailbox permissions.
Manual Registration Steps
Select the required method and follow the steps below to register the app manually.
Modern Method (Microsoft Graph API)
Step 1: Register App
- Log in to the Microsoft Entra ID Admin Center (Azure Active Directory) using your administrator account.
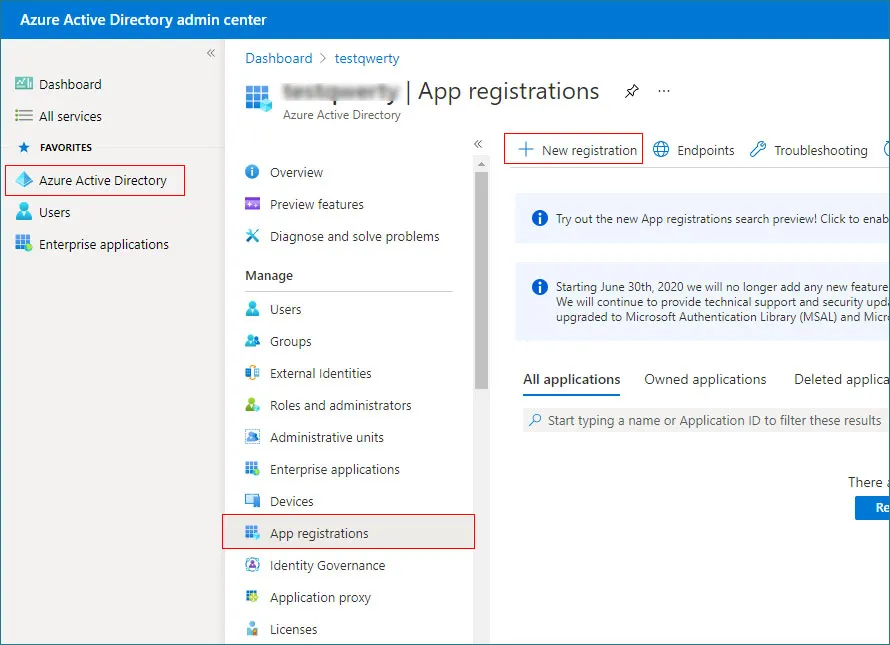
- Navigate to Entra ID, then select App registrations, and click + New registration.
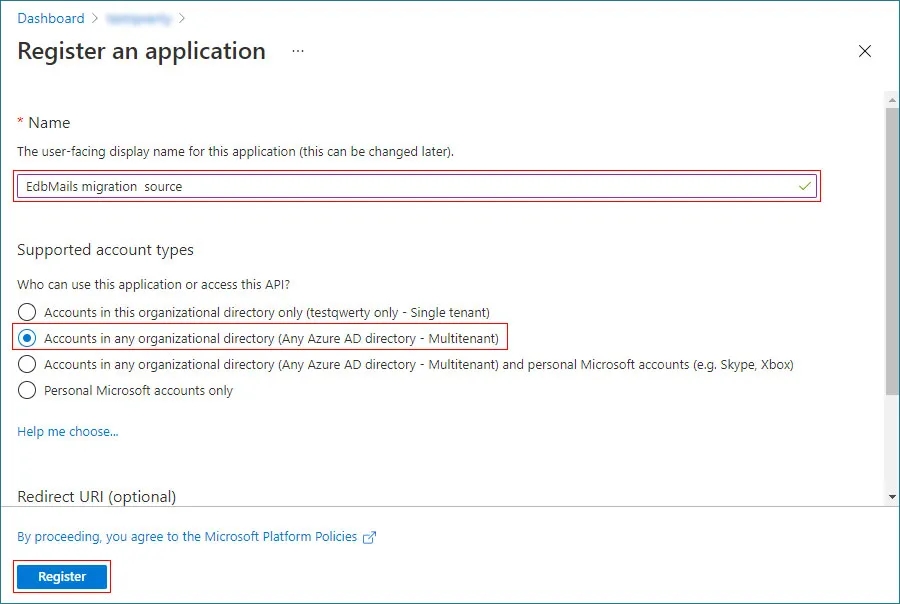
- Next, enter the display name for the application, and select the type of account to use. For example, for account type select Accounts in any organizational directory (Any Microsoft Entra ID tenant - Multitenant) on the registration window, and then click Register.
Steps 2: Configure the application permissions
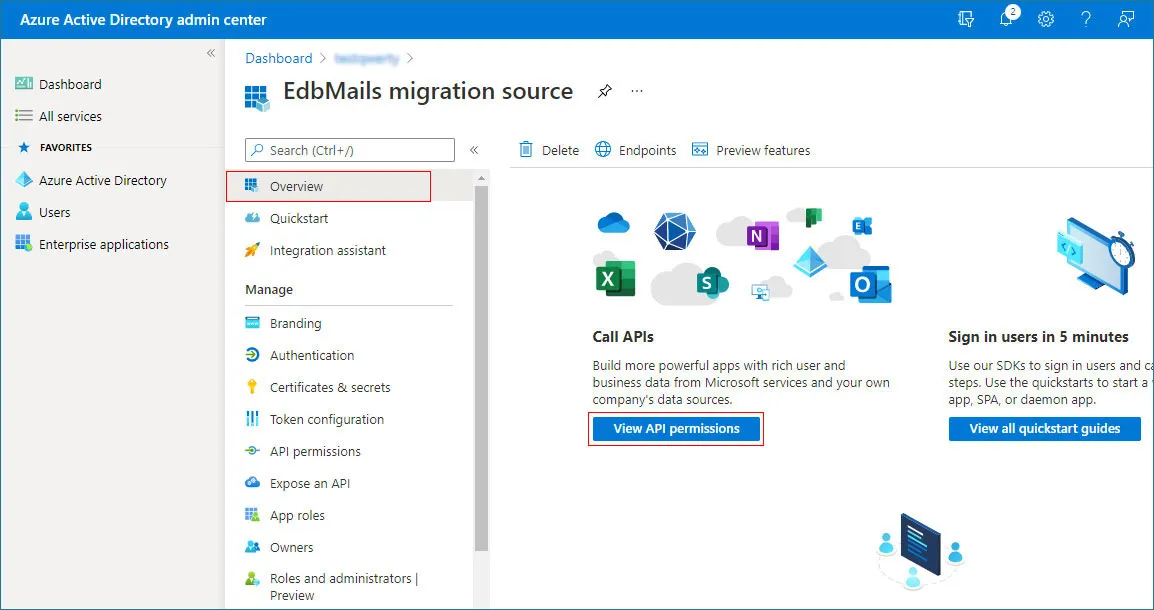
- On the application’s Overview page, click View API permissions to access and manage the app’s permission settings.
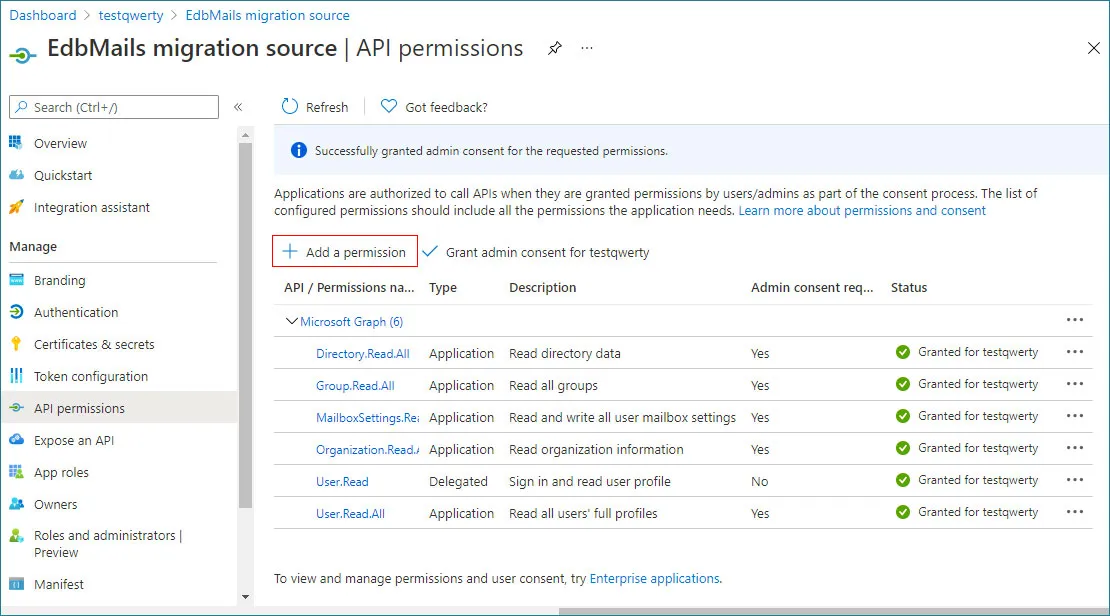
- Click the + Add a permission button in the API permissions page
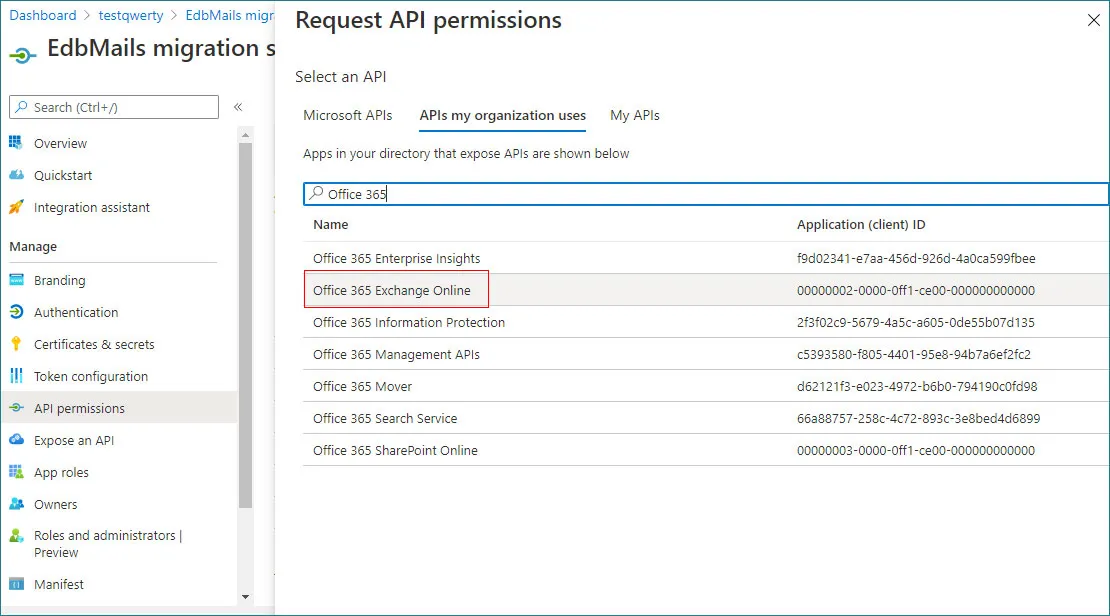
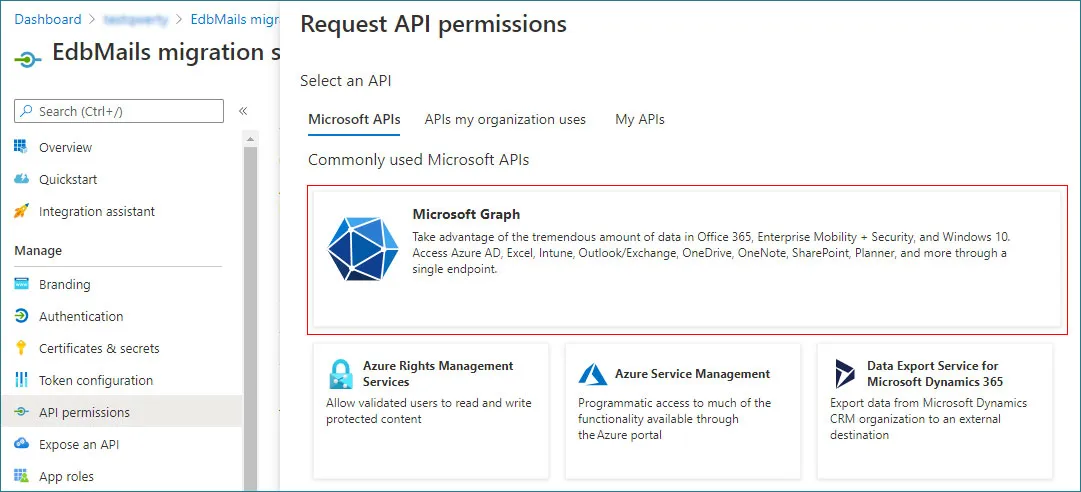
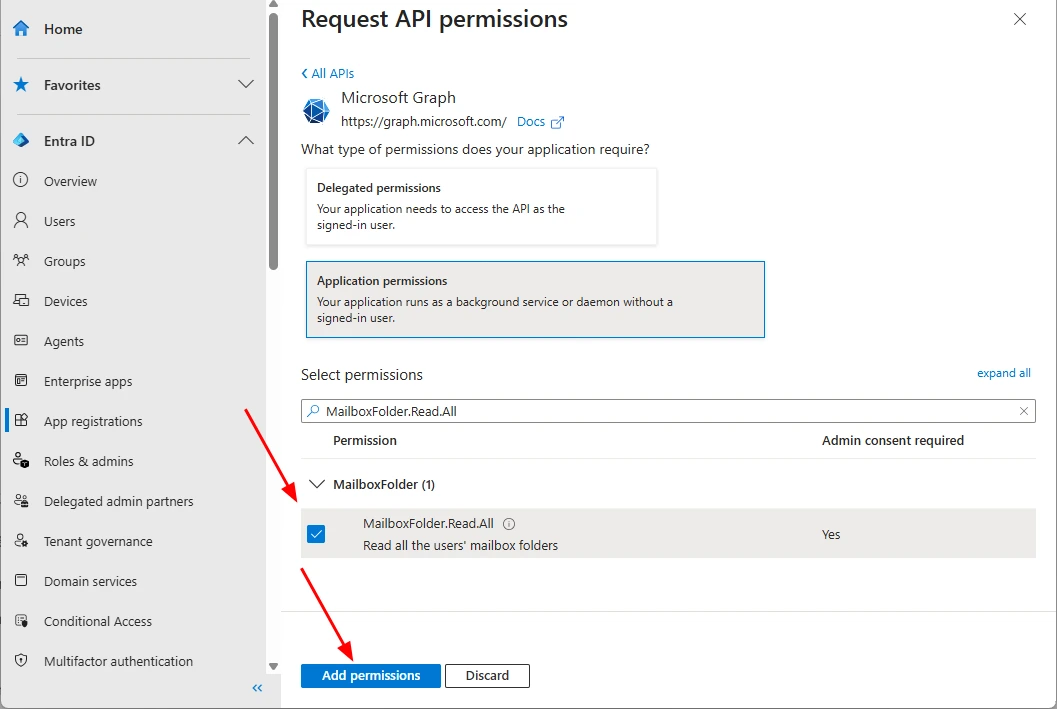
- Next, in the Request API permissions window, choose Microsoft Graph from the Microsoft APIs section.
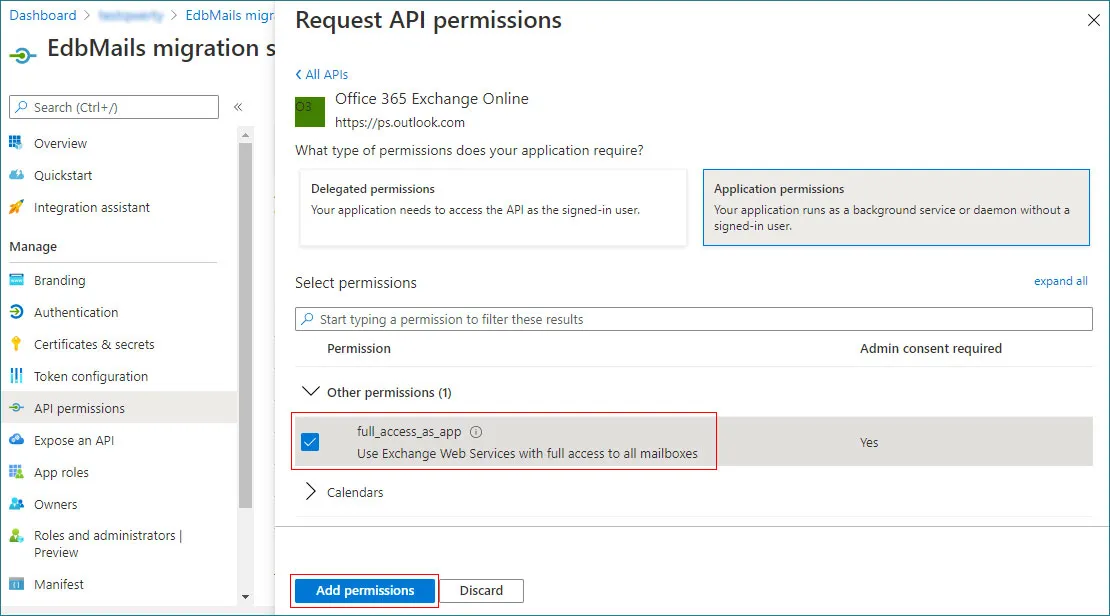
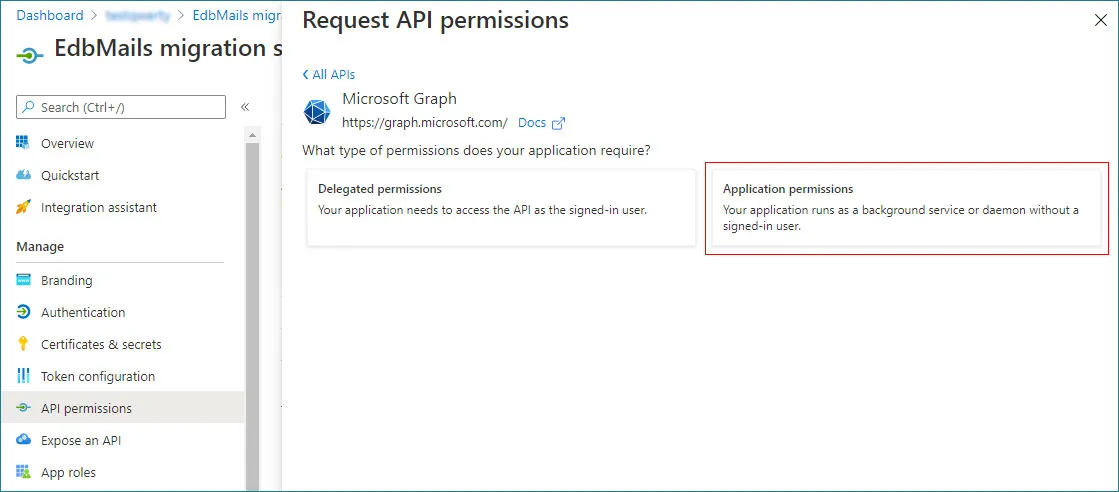
- Then, choose Application permissions from the available options.
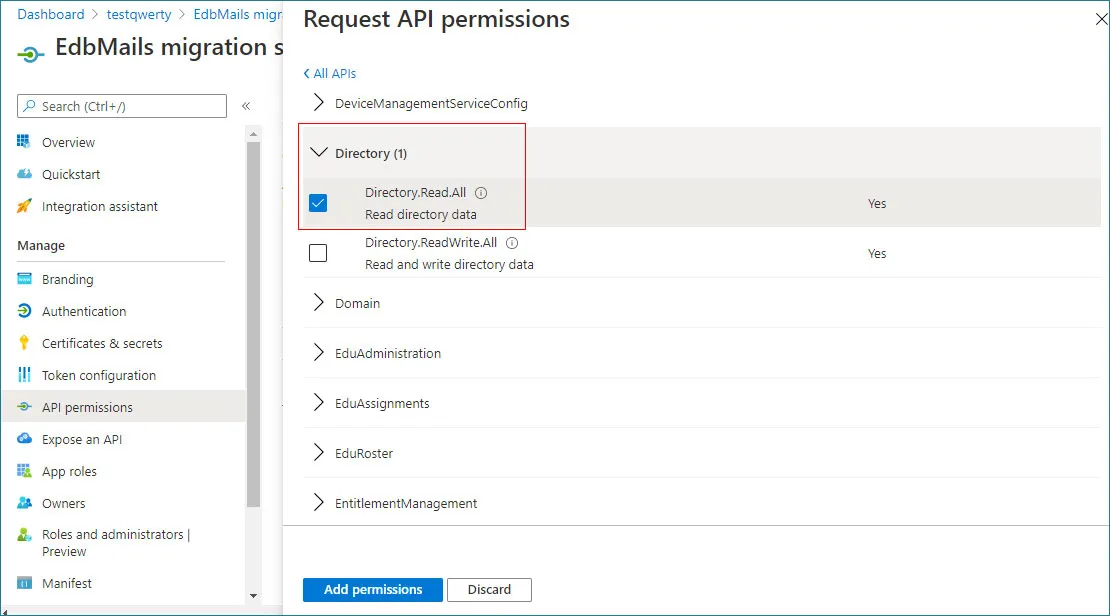
- Choose the following permissions from the list and click Add permissions to apply them.
Connection to Source Exchange Online (If the app registration is for source account)
- MailboxFolder.Read.All
- MailboxItem.Read.All
- MailboxItem.Export.All
- User.Read.All
- People.Read.All
- Contacts.Read
- Notes.Read.All
- Tasks.Read.All
- Calendars.Read.All
- Mail.Read
Connection to target Office 365 (If the app registration is for target account)
- MailboxFolder.ReadWrite.All
- MailboxItem.ReadWrite.All
- MailboxItem.ImportExport.All
- User.Read.All
- Contacts.ReadWrite
- Notes.ReadWrite.All
- Tasks.ReadWrite.All
- Calendars.ReadWrite.All
- Mail.ReadWrite
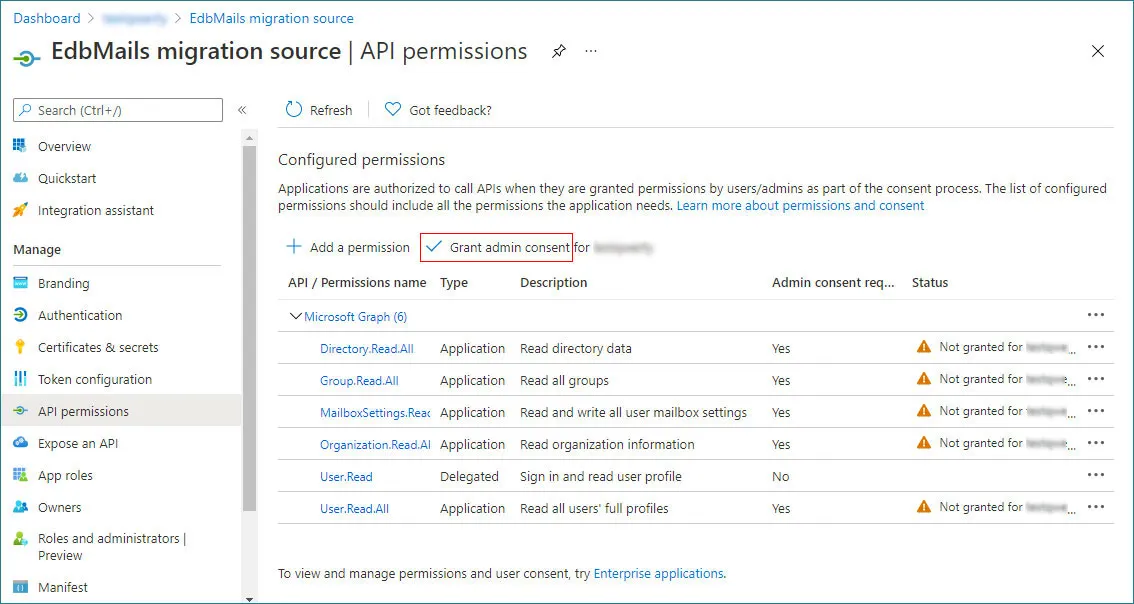
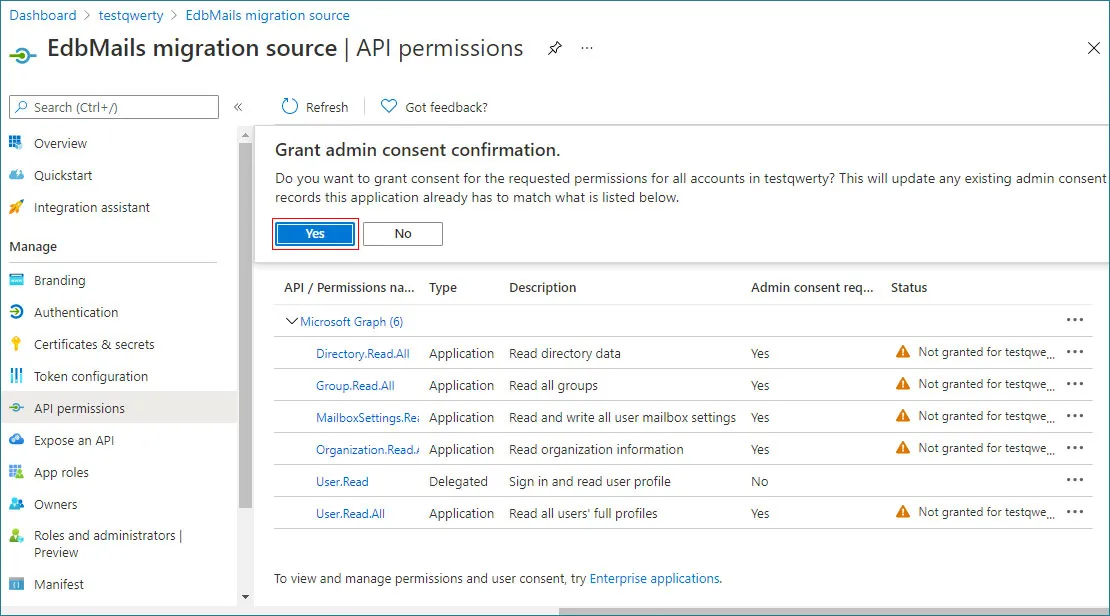
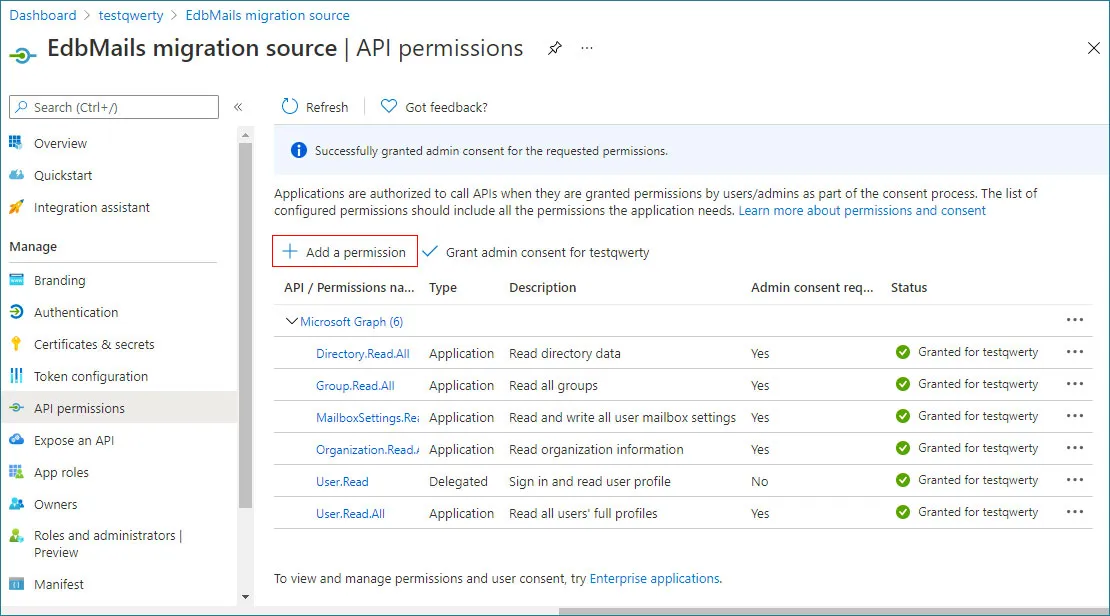
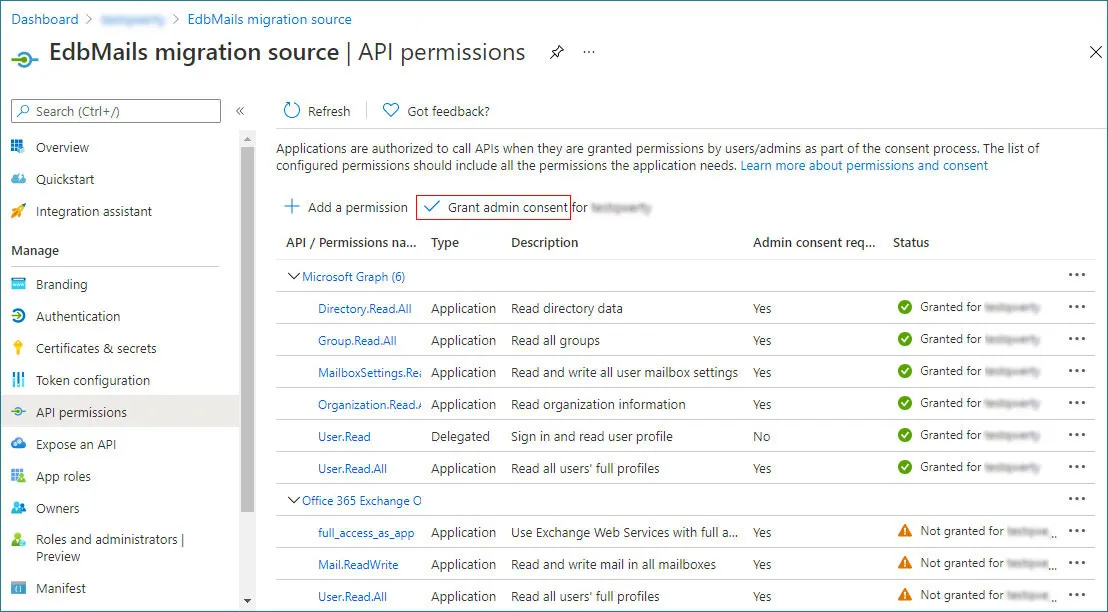
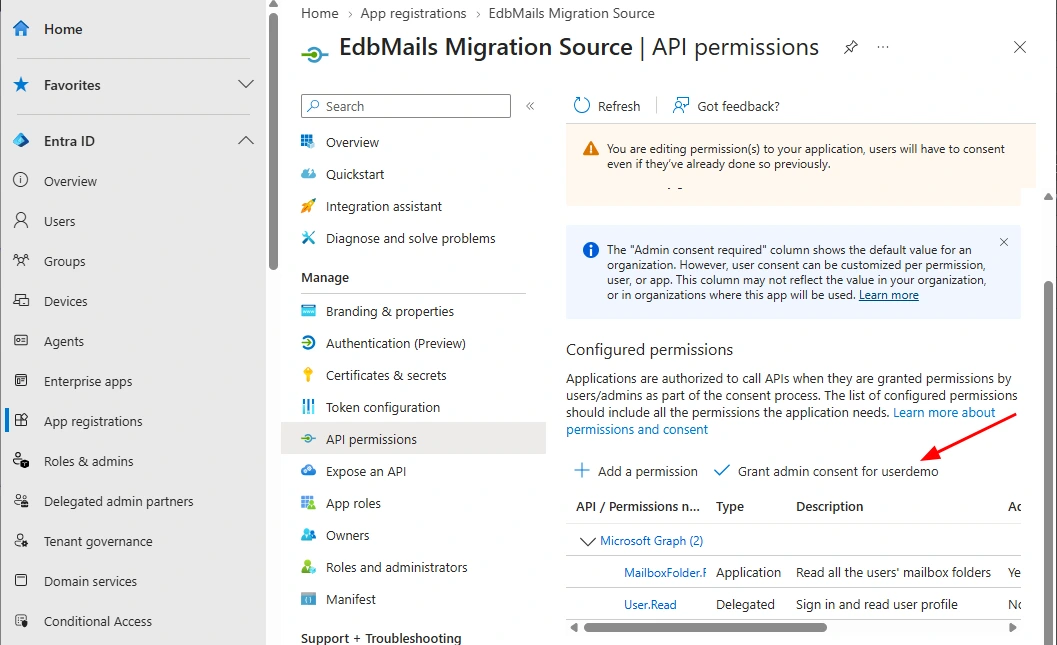
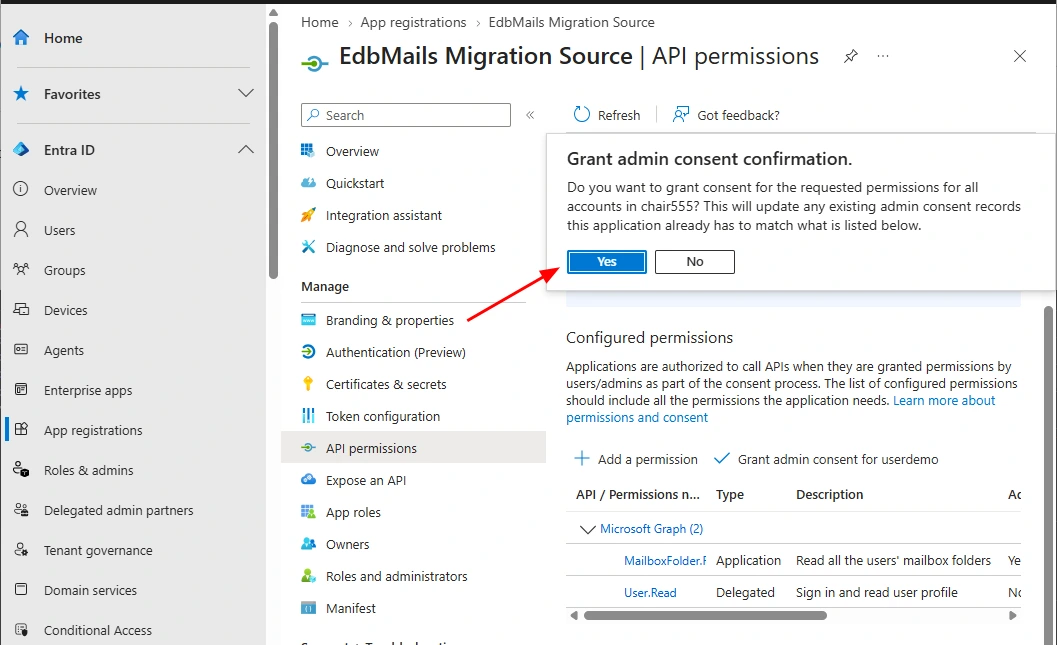
- On the API permissions page, click Grant admin consent for userdemo and confirm by selecting Yes.
Step 3: Add client secrets to the application in Azure AD
It is necessary to add client secret to the newly created application. It allows the OAuth protocol to prove the apps existence. Follow the below steps to add a client secret to the EdbMails application which is registered in Azure AD.
- Go to Entra ID and then select App registrations. Now select the newly added application
- Click on the Certificates & secrets and click on the + New client secret
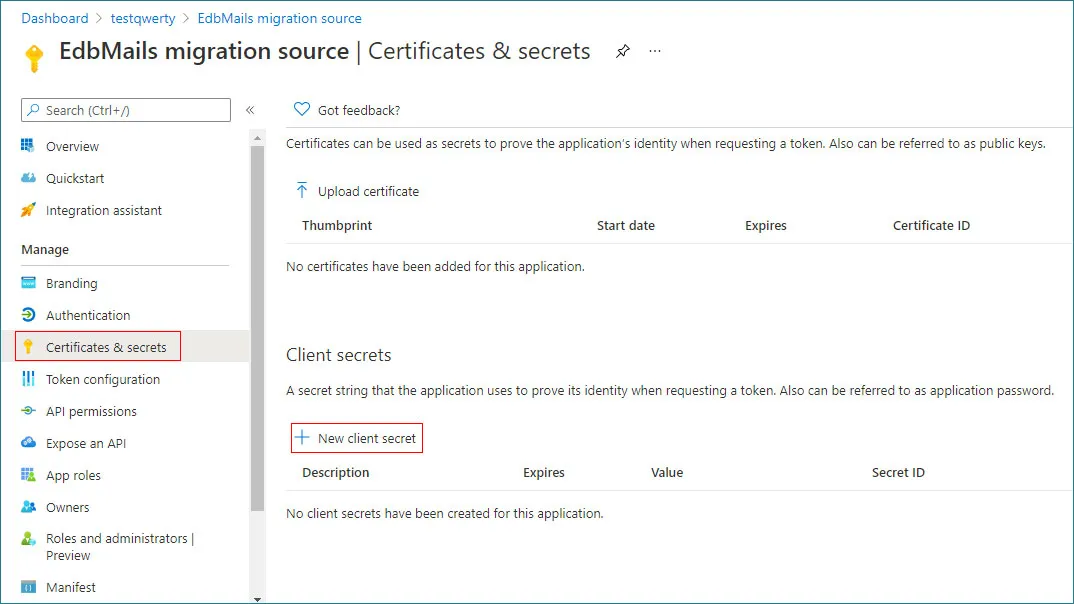
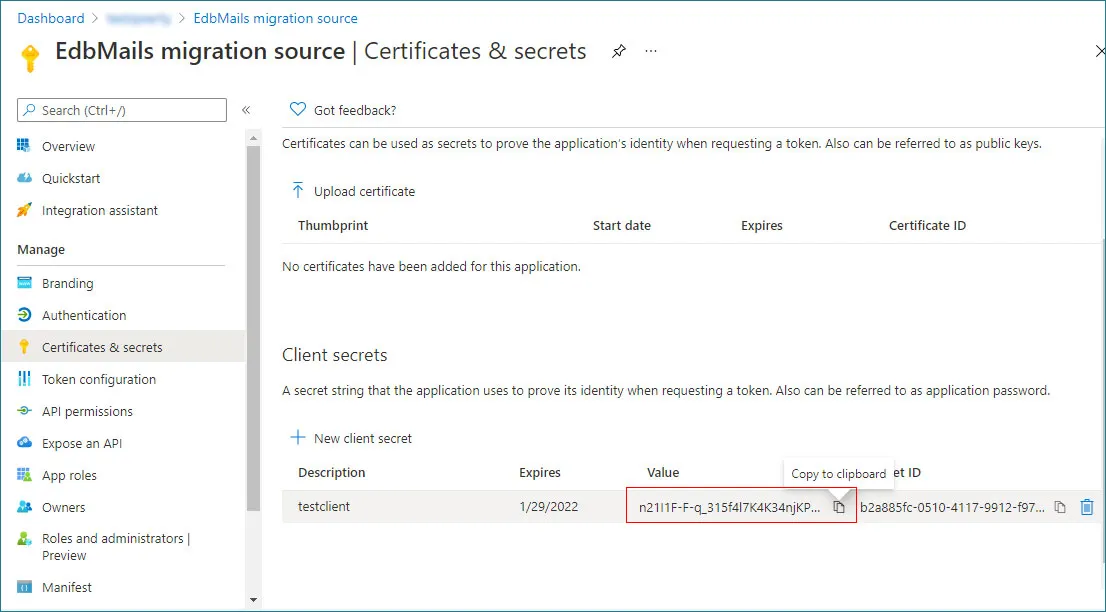
- Enter a brief description, choose the desired expiration duration, and then click Add to generate the secret.
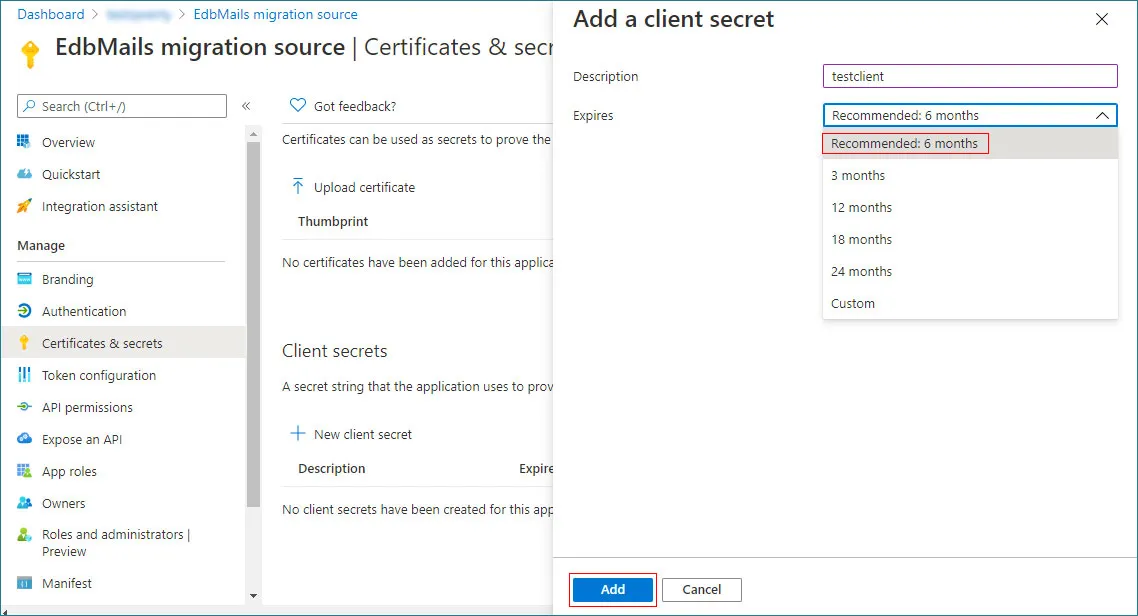
Note: Copy the client secret value to the clipboard or directly use it in the EdbMails application. Once you leave the page, the value will not be displayed again. Then you need to create another client secret.
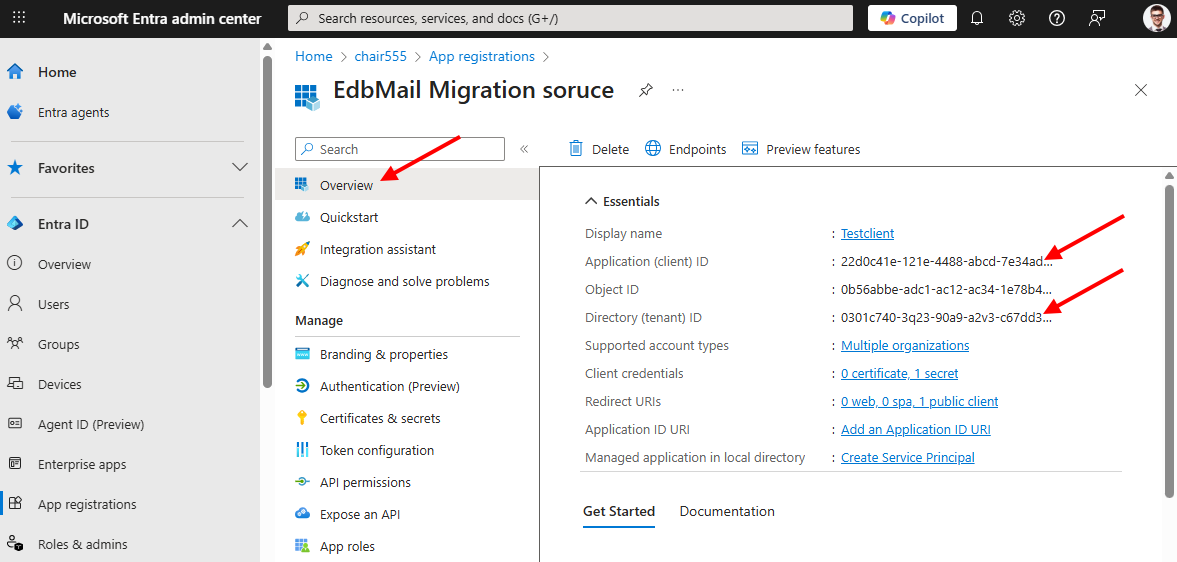
- Navigate to the 'Overview' section to copy the 'Application (Client) ID' and 'Directory (Tenant) ID', then paste them into the EdbMails application.
Step 4: Fill in the necessary registration details for Login in EdbMails
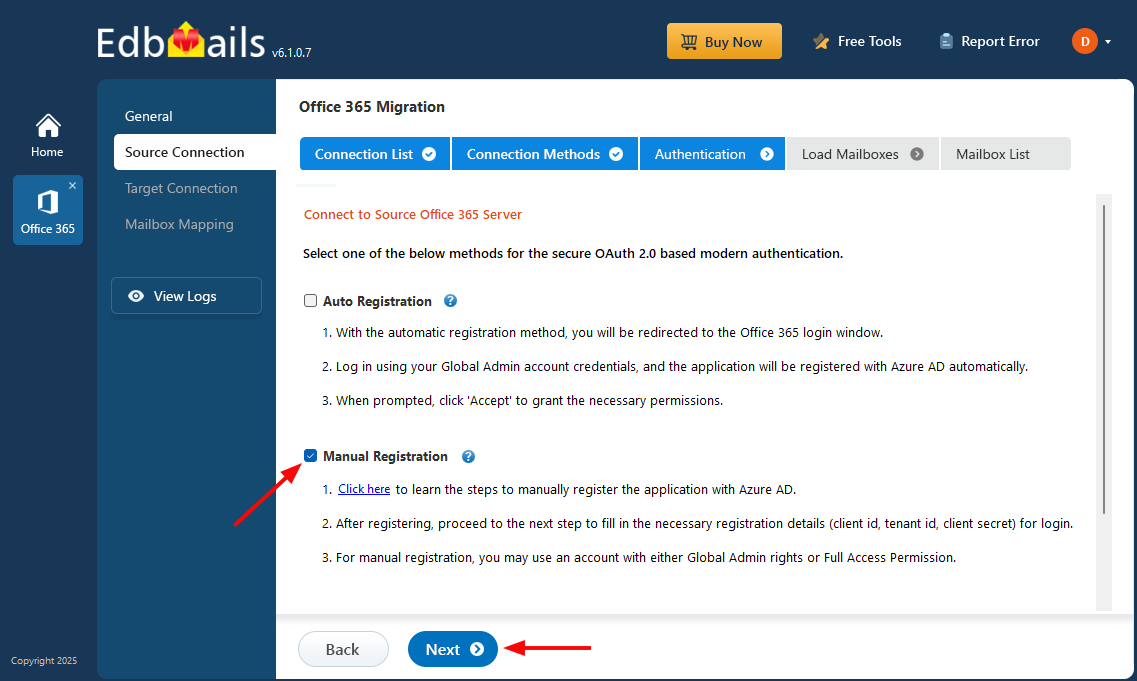
- Check the option 'Manual Registration' in the wizard and click the 'Next' button.
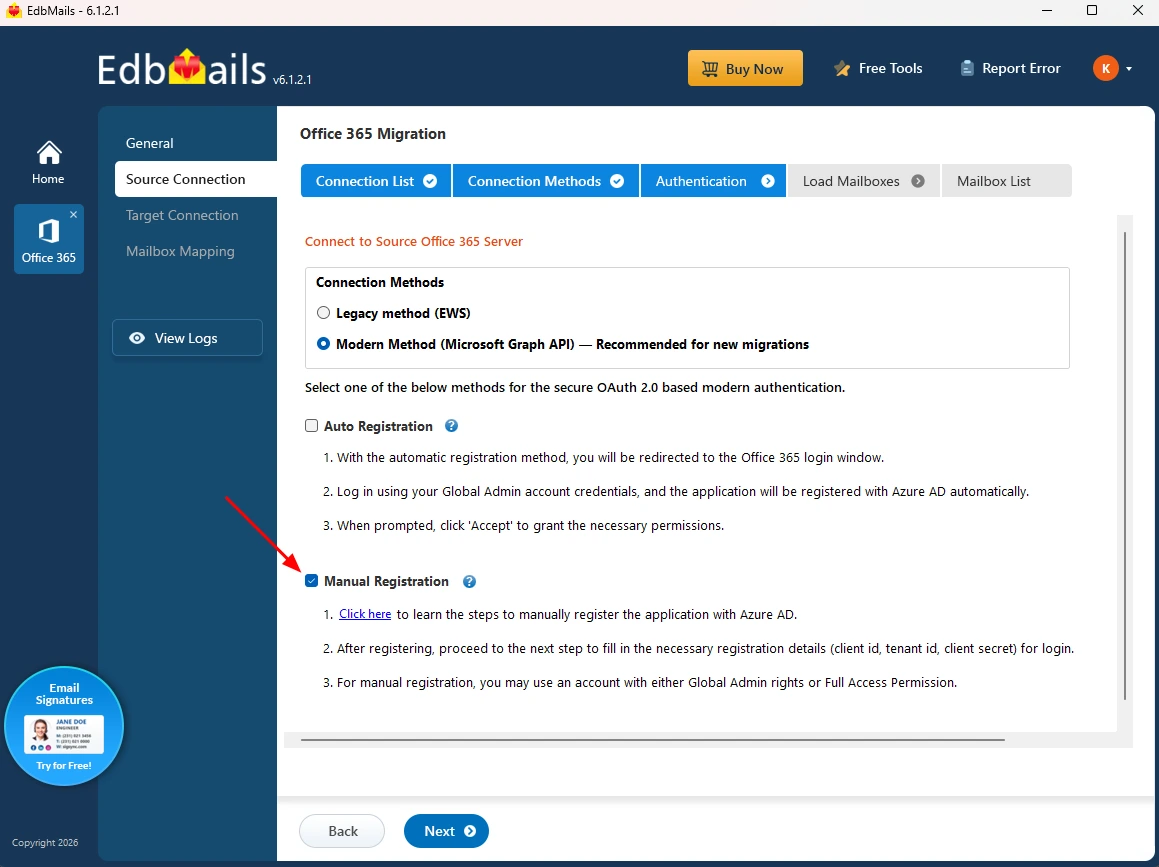
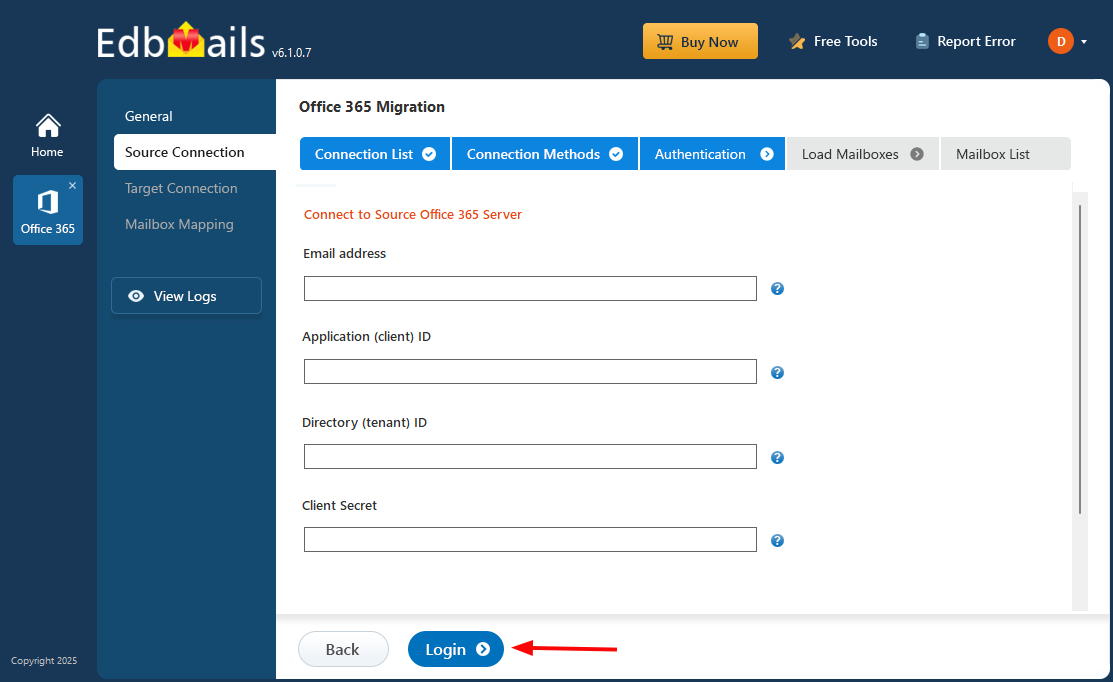
- Now enter the 'Email address', 'Application (client) ID', 'Directory (tenant) ID' and 'Client Secret' and click on the 'Login' button
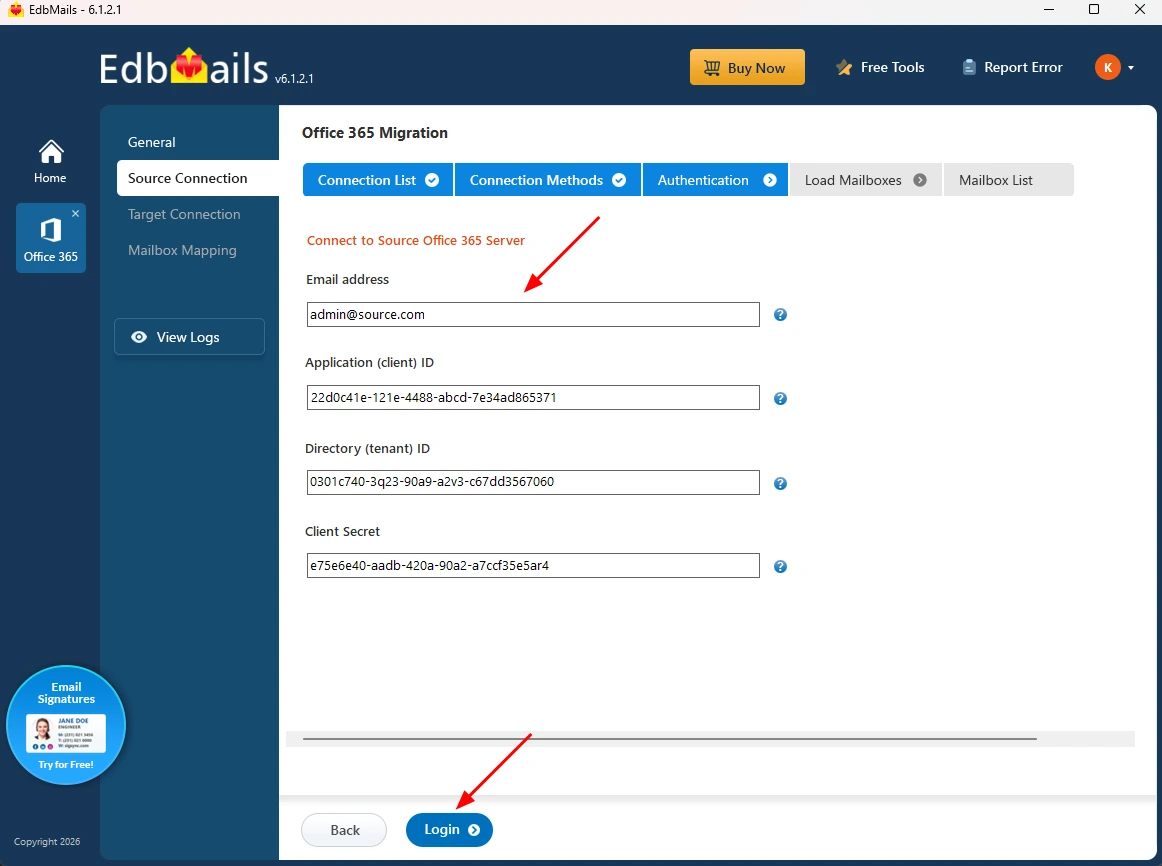
Note: Follow the above steps for the Source and Target Office 365 servers separately.
Legacy Method (EWS)